
Platforms:
Corelight provides deep network visibility by monitoring all network traffic (including cloud, encrypted, and internal traffic) to detect hidden attacks that traditional tools may miss.
It uses AI and machine learning combined with behavioral analytics and threat intelligence to identify suspicious patterns and advanced cyber threats.
It converts network activity into structured “evidence” that helps security teams investigate incidents with clear proof instead of just alerts.
It includes an Open NDR (Network Detection & Response) platform that combines intrusion detection, packet analysis, and threat hunting in one system.
It supports automated triage using AI, where alerts are grouped, analyzed, and explained to reduce manual investigation work.
It integrates with security tools like SIEM, SOAR, and cloud platforms to improve enterprise-wide threat detection and response.

Jigso is an innovative AI-powered tool designed to transform fragmented information into structured, actionable insights.
Noah is a domain-focused AI research assistant built mainly for life sciences, healthcare, and biotech professionals.
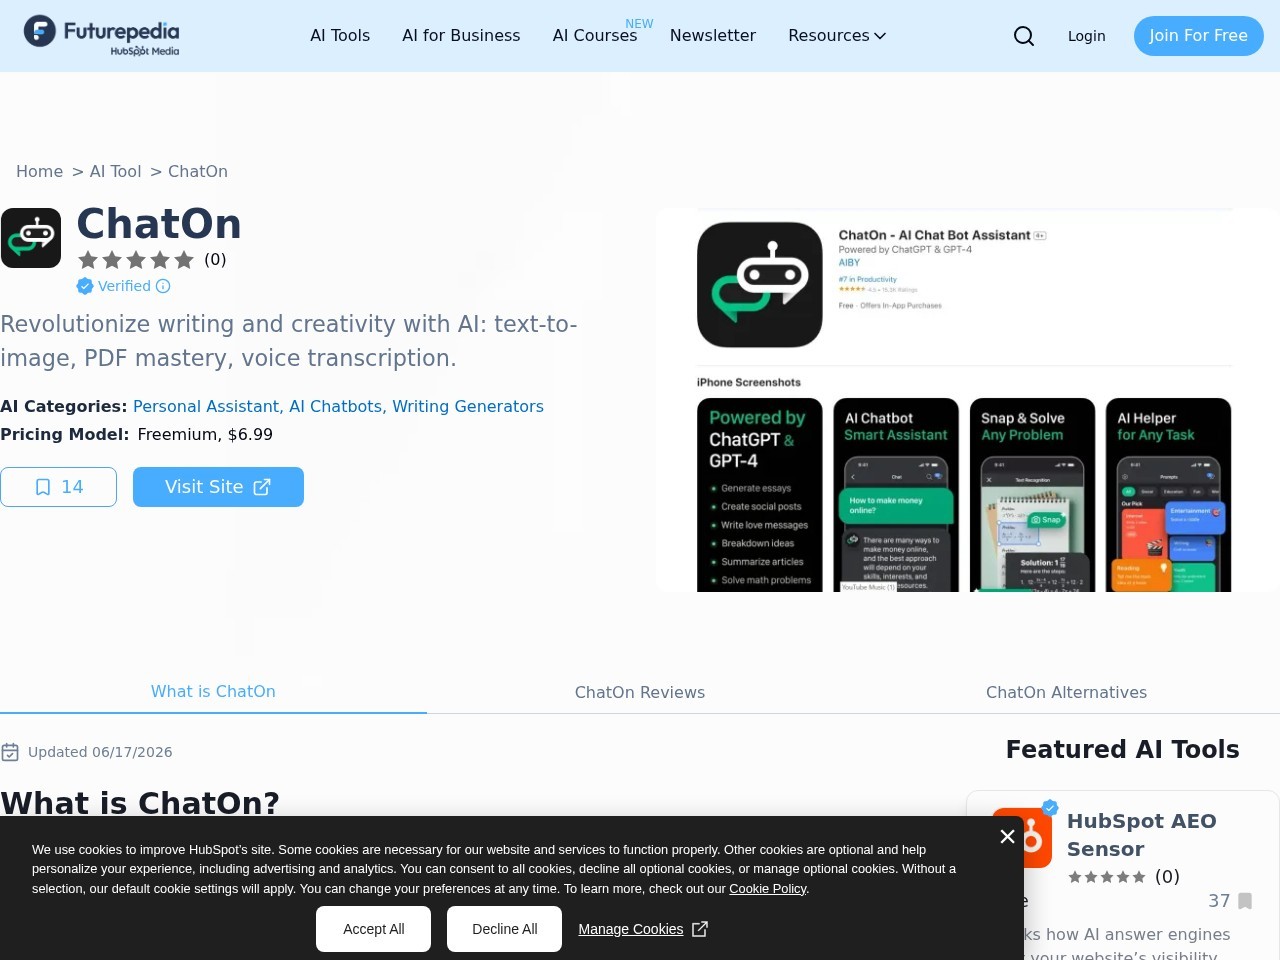
ChatOn is an all-in-one AI assistant that combines multiple AI models and tools into a single chat-based platform.

EvenUp Law is an AI-powered legal platform built specifically for personal injury law firms to automate demand packages and medical case documentation.
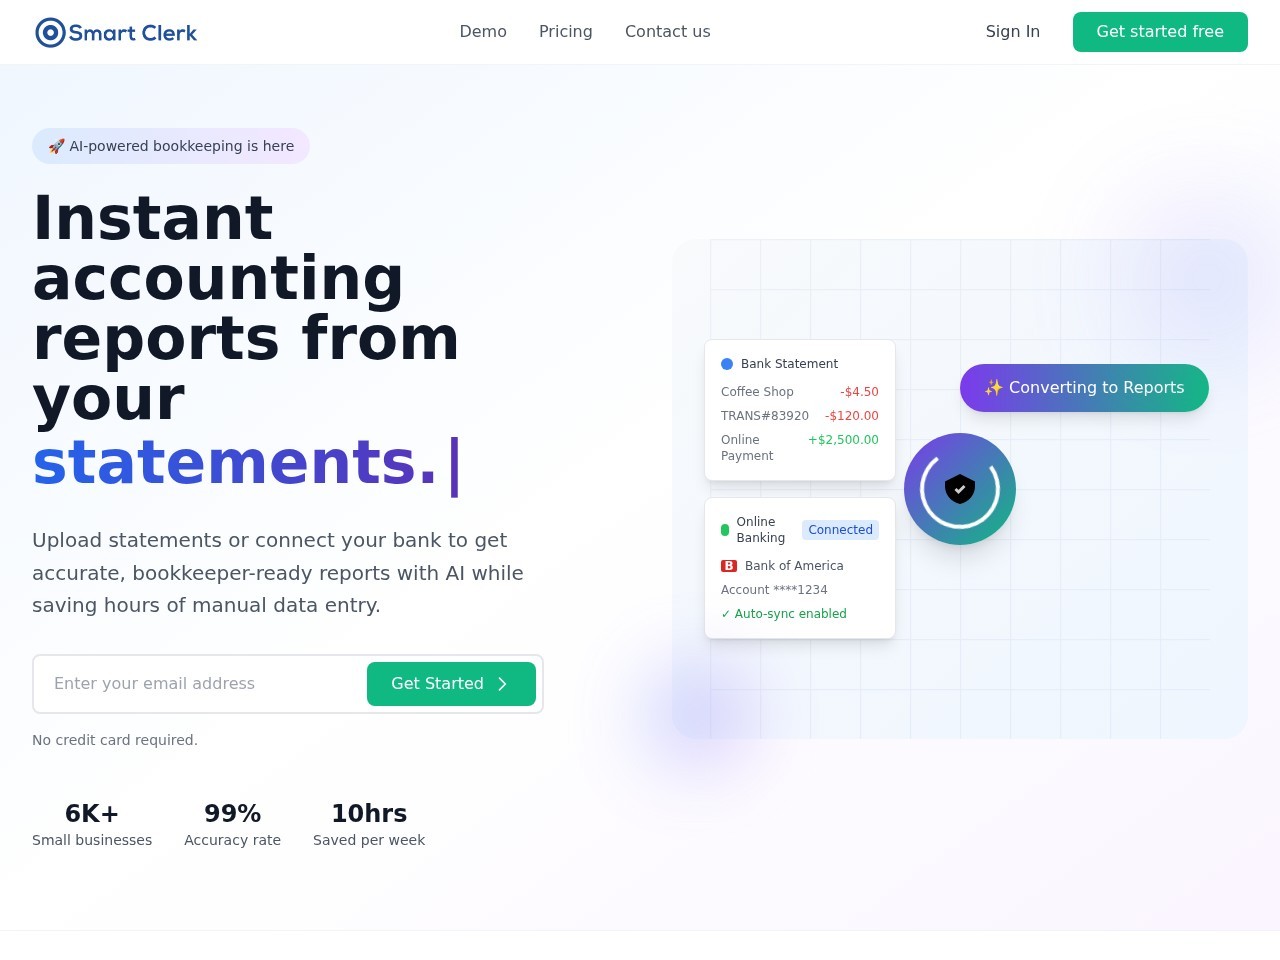
Smart Clerk is an AI-powered accounting automation tool that converts financial documents like bank statements, invoices, and receipts into structured, ready-to-use reports.
Enso is an AI-powered business automation platform that helps companies streamline operations by connecting tools, data, and workflows into one intelligent system.